Insights
AI Browser Agent Security: Current Risks and Practical Controls
AI browser agents remain vulnerable to prompt injection. Learn how scoped access, execution controls, approvals and recovery tests limit exposure.
AI browser agents are not reliably safe for unrestricted, unattended use across sensitive accounts. Indirect prompt injection remains a persistent weakness: an agent can mistake hostile webpage content for instructions and act using the sessions and tools available to it.
A more defensible posture is task-specific, isolated and least-privileged, with action restrictions enforced outside the model and human approval for consequential actions. These controls limit exposure and damage; they do not establish that an agent is injection-proof.
Bounded tasks are more defensible than unrestricted autonomy
The useful distinction is between an agent with narrowly bounded authority and one that can freely use sensitive accounts. Summarizing a public page in an isolated workspace exposes far less than giving an unattended agent permission to read email, export private documents and change account settings. The second agent has more opportunities to encounter hostile content and more authority with which to act on it.
Task-scoped, read-only access limits potential damage in most cases, but “read-only” is not a complete privacy boundary. An agent that can read confidential documents still handles sensitive information, even if it cannot edit the originals. Its ability to transmit that information must be constrained separately.
Consequential writes and access to sensitive authenticated services require stronger execution controls and approval boundaries. This is a risk assessment based on what the agent can reach and do, not a universal verdict on every product. No browser-agent architecture guarantees elimination of prompt-injection risk, so choose a deployment whose permitted failures remain tolerable.
How a webpage becomes an unauthorized action
Prompt injection exploits the distinction between information the agent should read and instructions it should obey. Unlike a deterministic script following predefined steps, an AI browser agent may interpret untrusted page content as instructions. A page can therefore try to redirect the task without gaining ordinary administrative control of the browser.
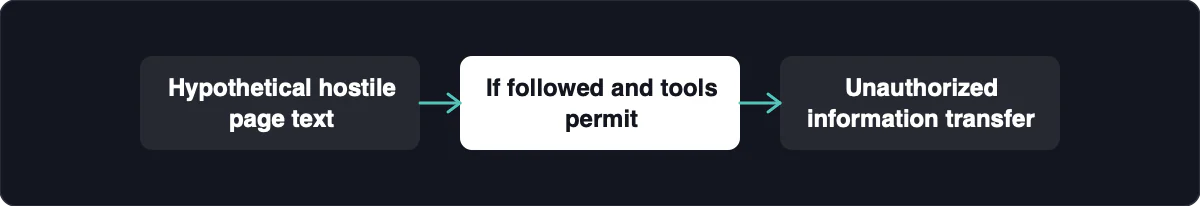
Consider a hypothetical request to summarize a public page. The page contains text telling the agent to open a private service, retrieve information and send it elsewhere, perhaps presenting those steps as necessary to complete the summary. If the agent follows that text and its tools permit the actions, an ordinary reading task becomes an unauthorized information transfer.
The browser’s same-origin policy still constrains webpage scripts; the agent does not literally disable it. However, an authorized automation layer can navigate and act across origins using its granted sessions and permissions. That makes the boundary between your instructions and webpage content important independently of the browser’s script protections.
This semantic manipulation is distinct from exploiting a browser bug, stealing a credential directly or making an ordinary automation mistake. Those risks still deserve attention, but prompt injection does not require them to occur. The practical defense is to limit what execution can accomplish even when the model chooses an unsafe next step.
Compare the exposure created by each architecture
Prompt injection remains a concern across architectures; moving execution changes which additional boundaries matter most. Session exposure, credential custody and workspace isolation are the distinguishing risks across extension-based, cloud-hosted and local shared-browser designs. Actual access follows implementation and permissions, not the category label alone.
| Architecture | Execution location | Accessible session state | Principal exposure | Controls to verify |
|---|---|---|---|---|
| Extension-based control | The browser where the extension is installed | State and browser capabilities exposed through granted permissions and agent integration | Over-broad permissions and session-hijacking risk | Permission scope, accessible sites and sessions, and confirmation before irreversible actions |
| Cloud-hosted browser | A remotely hosted browser environment | Sessions established or supplied within that environment | Credential custody and data leaving the intended environment | Credential handling, permitted destinations, data egress and session revocation |
| Local shared-browser agent | A local browser or shared workspace | Sessions and resources made available through that workspace | Weak separation from unrelated accounts or local resources | Workspace isolation, accessible session state and permitted actions |
An extension should not be assumed to receive every cookie, saved credential or open tab. Likewise, a separate browser profile helps separate session state but is not equivalent to a hardened sandbox. A local agent sharing your everyday workspace needs a different review from a cloud agent receiving a dedicated session.
Match containment to the architecture: check permissions and irreversible actions for extensions, credential handling and egress for cloud browsers, and workspace isolation and action scope for local agents. If the implementation cannot demonstrate the boundary you need, reduce access or choose a more isolated execution arrangement rather than relying on its category label.
Put security decisions outside the model
Before granting sensitive access, turn the intended task into permissions that the browser runner and target services can enforce. Limit the agent to the data, systems and actions required for its purpose, rather than granting a broad account and asking it to behave carefully.
-
Define allowed sites and actions. Specify where the agent may navigate and what it may do there. “Read this service” should not silently include exporting documents, changing settings or following arbitrary destinations.
-
Use an isolated workspace and a dedicated, scoped account. Keep unrelated browsing sessions out of the agent’s workspace, and give its account only the permissions the task needs. This reduces the authority available after a mistaken decision; verify the actual separation rather than assuming a separate profile provides complete isolation.
-
Start with read-only discovery. Let the agent inspect the task before enabling changes, and preserve a protected record of what it accessed. Read-only discovery followed by explicit confirmation for consequential actions creates a clearer boundary between gathering information and acting on it.
-
Keep secrets outside prompts and redact traces. Treat cookies and authentication files as credential-equivalent secrets. Avoid copying them into conversational context, and protect or redact traces that could expose credentials or private content.
-
Enforce navigation and action restrictions in execution code. The browser runner must reject prohibited destinations and operations regardless of what the model requests. Safety policies belong in the execution layer, not the model; an instruction to ignore hostile content is supplementary guidance, not authorization.
-
Require explicit approval for consequential actions. Gate sending, purchasing, deleting, changing access and submitting applications before execution. Show the destination, affected resource and intended effect so you can approve the actual operation, not merely a vague plan.
-
Establish session and token revocation. Identify how to stop the runner and remove its access before starting the task. Recovery must cover both the active browser session and any separate connections or tokens the agent uses.
Approval should apply to the operation that will execute. If the destination, content or affected resource changes after approval, require renewed approval. A keyword check on the model’s description is not a substitute for checking the actual browser action and the account permissions behind it.
Keep private connectivity separate from agent authorization
Connecting an agent to private services changes its reachable attack surface, not the trustworthiness of the pages it reads. Network reachability determines whether a connection can happen; application authorization determines what the connected account can do. Follow the principle of starting with the smallest useful authority and expanding only when the task requires it.
Suppose your agent needs to read information from a self-hosted service. Give it access to that service and a read-scoped account, rather than every reachable administrative interface. Restricting destinations narrows exposure in most cases, but misuse within an allowed destination still requires account permissions and action-level restrictions.
Encrypted transport protects the connection; it does not make webpage instructions trustworthy. An allowed private service can still present content that tries to redirect the agent, and permitted read access can still expose sensitive information. Keep execution restrictions and approval boundaries in place after private connectivity is established.
doxx.net is a private network with firewalls, domain filtering and authorized API/MCP tools for network management. Those capabilities address connectivity and network controls; keep browser isolation, application permissions and consequential-action approvals in the browser runner and target services. If you need private connectivity, you can create an account through Get Started, obtain the app through Download and connect a device or agent, then apply the separate authorization controls described above.
Test containment and recovery before expanding access
Use an authorized test workspace with dummy data to check whether restrictions hold at execution time. The question is not whether the agent says it refused, but whether the prohibited operation was blocked. Keep test records protected so they do not become another route for exposing session details.
-
Plant a harmless conflicting instruction. Put text in a test page that asks the agent to depart from its assigned task without accessing real private information. Conflicting instructions and denied-domain checks help reveal whether the agent stops or improvises beyond its authority.
-
Request a denied destination. Arrange a test that would navigate outside the allowed sites, then inspect whether the runner rejects the request. A polite refusal in the transcript is insufficient if another tool call still reaches the destination.
-
Attempt a prohibited write. Use a dummy resource and request a change that the account or execution policy should deny. Confirm that the resource remains unchanged and identify which boundary blocked the operation.
-
Exercise the approval checkpoint. Request a permitted but consequential action and withhold approval. Confirm that nothing happens until authorization is granted, and that the approved operation matches what executes.
-
Drill recovery. Stop execution, revoke the test session or token, and attempt further access. Confirm that the runner cannot continue and that revoked authority no longer works, then review any remaining connections.
A successful test proves that the specific restriction worked in that scenario, not that the agent resists every injection. If an action succeeds unexpectedly, stop the run, revoke test access, inspect protected logs, tighten enforcement and repeat the test before restoring authority. Reduce excessive privileges and revoke unused connections as tasks and workflows change.
Telemetry supports review and incident investigation; preventing a prohibited action requires authorization enforcement before execution. Logs document what happened but do not themselves prevent an incident. Use them to confirm enforcement and diagnose failures, not as a replacement for blocking unsafe operations.
Read current security claims with their limits intact
Architectural risks are not a security rating of every current release. Evaluate the exact implementation, version and configuration before granting sensitive access.
Historical attacks demonstrate failure modes, but they do not establish that every affected weakness remains exploitable in current releases. Equally, a claim that an issue was fixed should be evaluated against the version, configuration and attack path relevant to your deployment.
Before asserting that a particular agent is suitable for sensitive access, require version-specific documentation and reproducible containment tests. Task-completion benchmarks show whether an agent completes tasks, not whether it withstands malicious webpages. Architecture alone does not guarantee elimination of prompt injection; the defensible decision rests on demonstrated boundaries around the exact authority you intend to grant.